Web Dashboard — Manage AI in Browser
Web Dashboard — Manage AI in Browser — easy-to-understand guide based on official docs
Remember the days when changing your router settings meant memorizing IP addresses and typing cryptic commands? The Hermes Agent Web Dashboard is like swapping that command-line remote for a touchscreen panel—you see a button, you click it. No memorizing flags, no editing YAML files by hand. Just point, click, and manage.
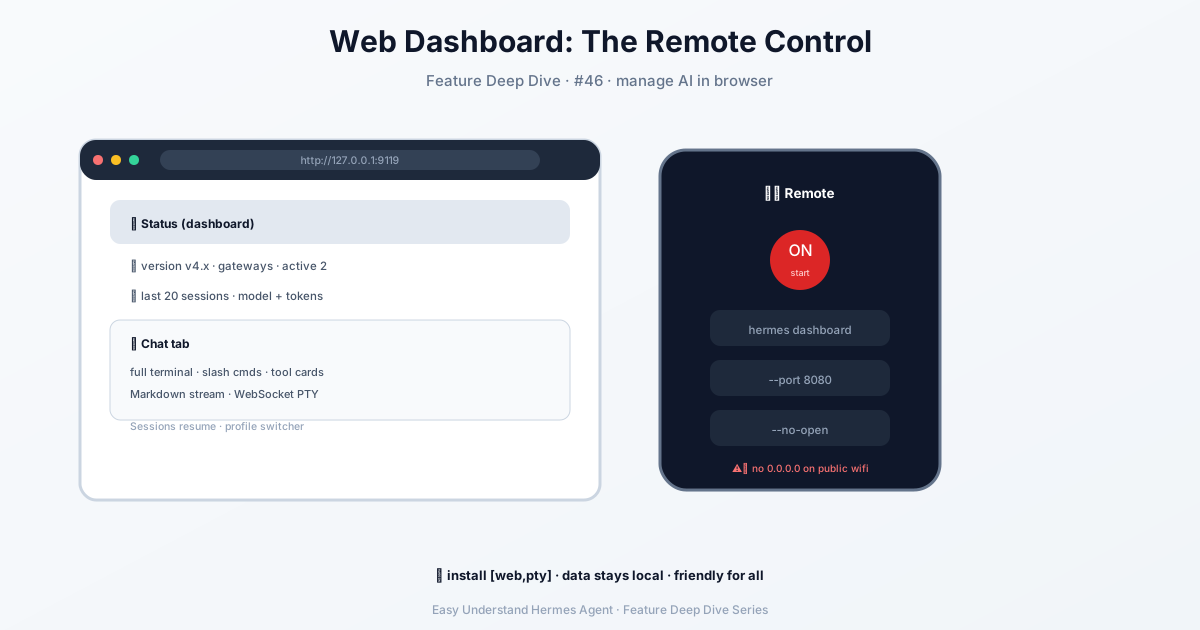
What Exactly Is It?
The Web Dashboard is a graphical interface that runs right in your browser. Previously, tweaking configuration, adding API keys, or reviewing chat logs meant opening a terminal and typing commands. Now, you open a webpage and interact with it like any modern app—fill in a field, toggle a switch, done.
Crucially, everything runs locally on your machine. Your data never leaves your computer, so there’s no cloud upload, no third-party server sniffing around. Privacy stays in your hands.
If you’re using hosted-mode auth, it runs through Nous Portal OAuth. And if you want the dashboard to talk to a real backend, hermes setup --portal wires up the model and tool gateway too—see https://hermes-agent.nousresearch.com/docs/integrations/nous-portal for details.
Hub actions (skill install/update/uninstall, MCP install, toolset setup) run with the target profile’s own secret scope — its .env and configured secret sources — not the dashboard process’s environment; this includes actions targeting the default profile from the machine dashboard.
Starting the Dashboard
Launching it is almost embarrassingly simple. Open your terminal and run:
hermes dashboardHit Enter, and Hermes starts a local server, then automatically opens your default browser to http://127.0.0.1:9119. If you see the interface, you’re in.
Handy Switches to Know
The default setup works great out of the box, but sometimes you need a tweak. Here are the most useful flags:
| What You Want | Flag |
|---|---|
| Use a different port (e.g., 8080) | --port 8080 |
| Don’t auto-open the browser | --no-open |
| Allow other devices on your LAN to access it | --host 0.0.0.0 (this forces password or OAuth login—that’s the security guard) |
| Run a dedicated per-profile server instead of routing to the machine dashboard | --isolated |
For example, to start on port 8080 without launching the browser:
hermes dashboard --port 8080 --no-openOfficial Dashboard Screenshots
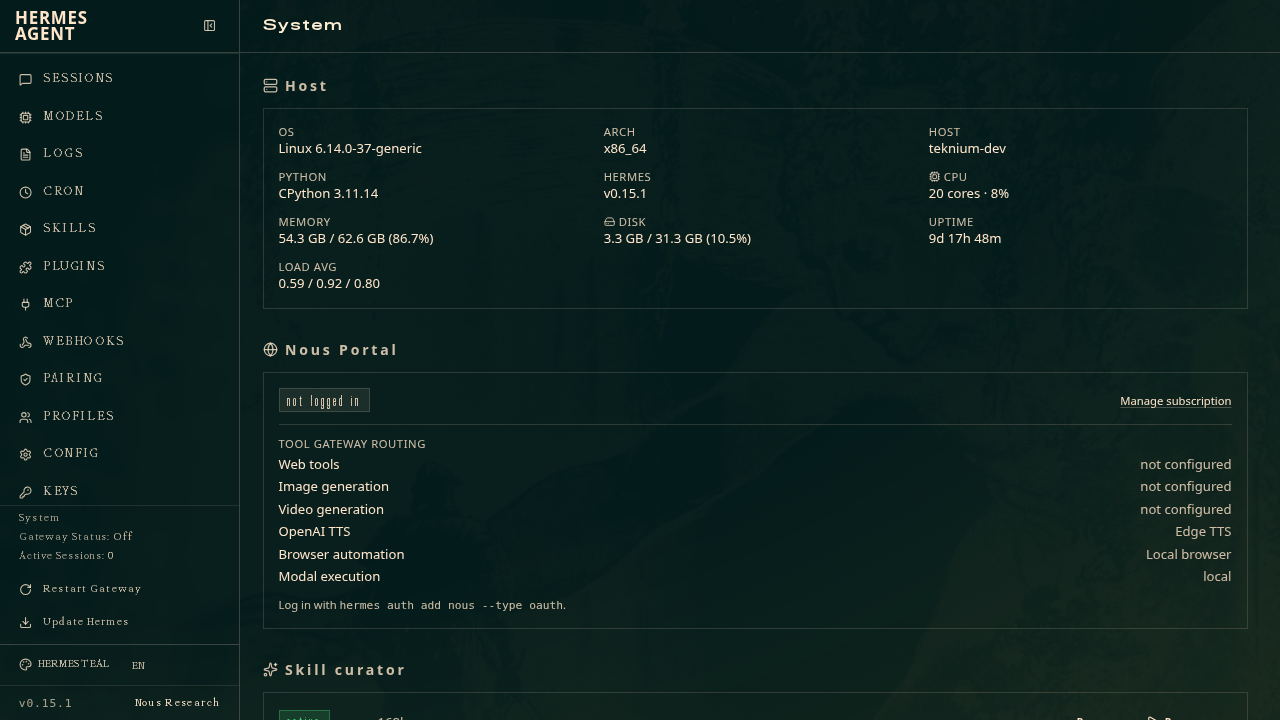
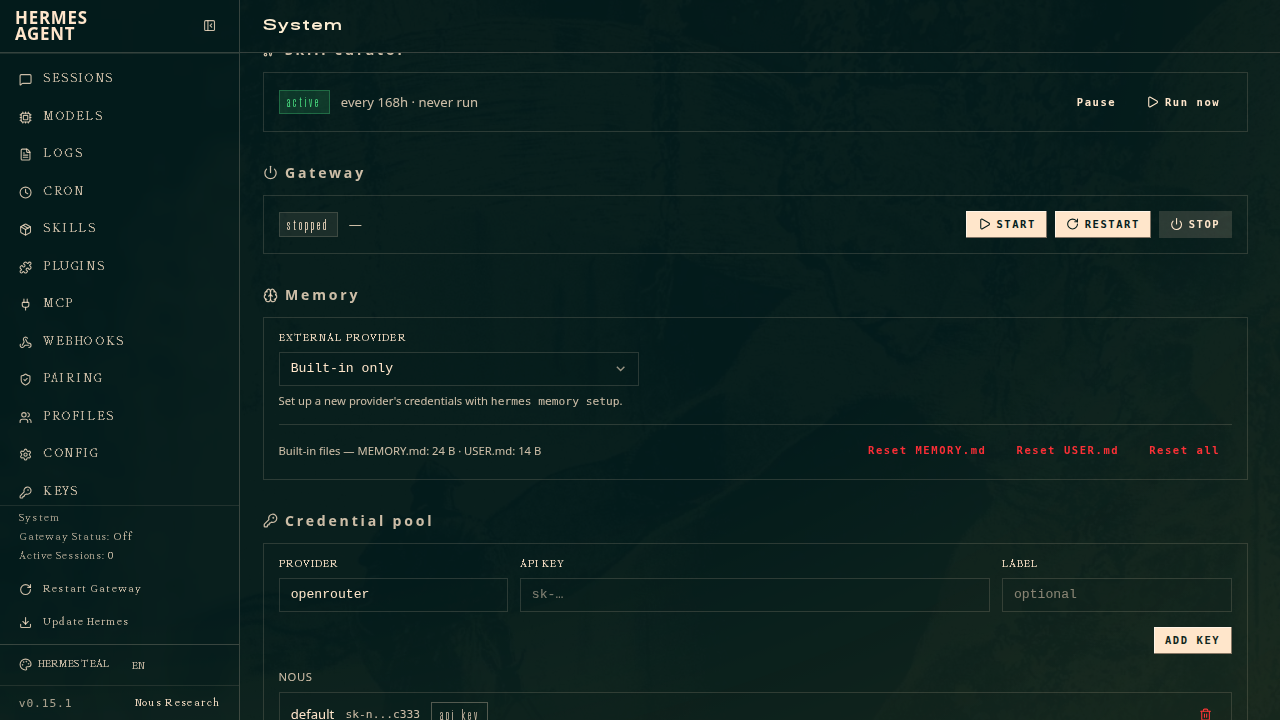
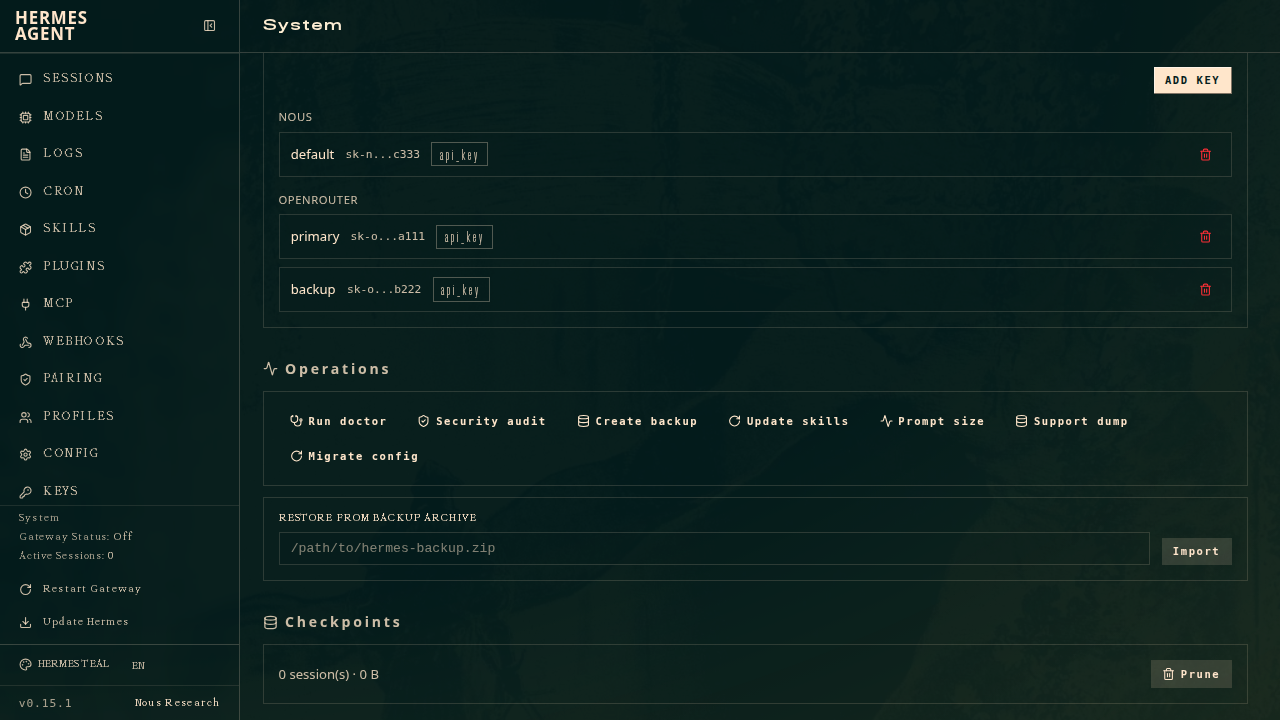
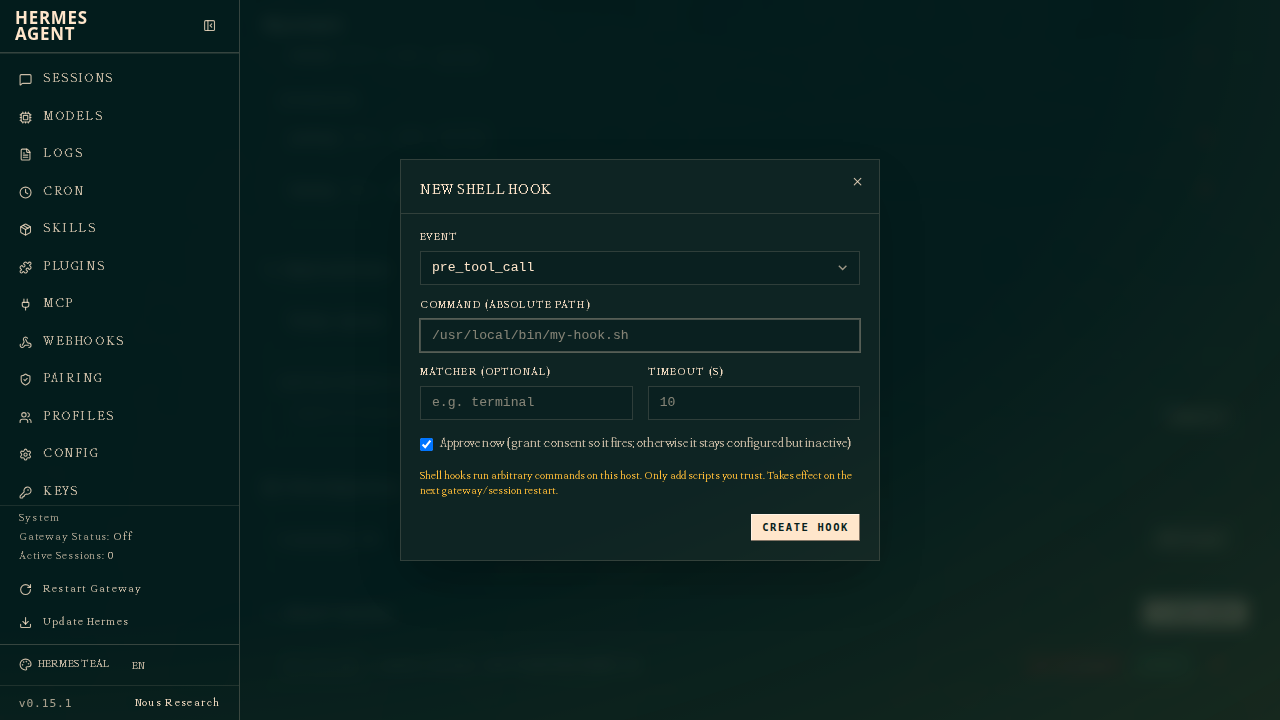
Here are the real admin pages from the official Web Dashboard, so you know what to expect:
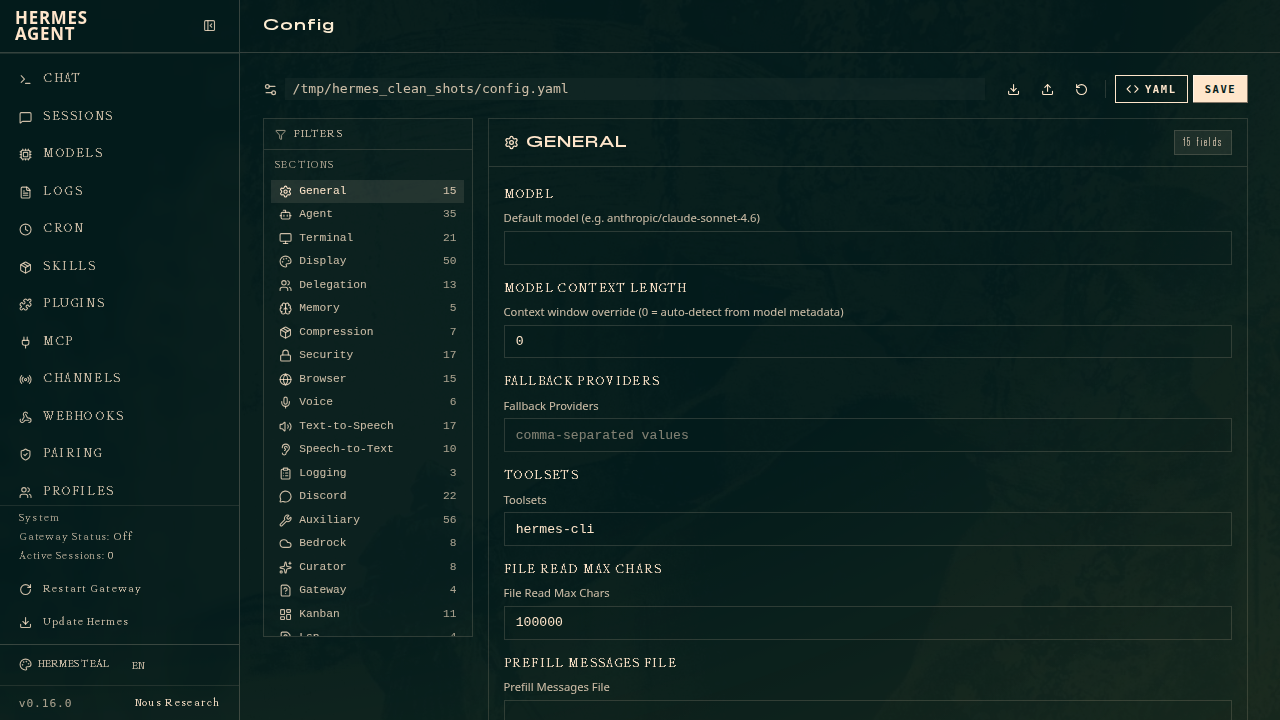
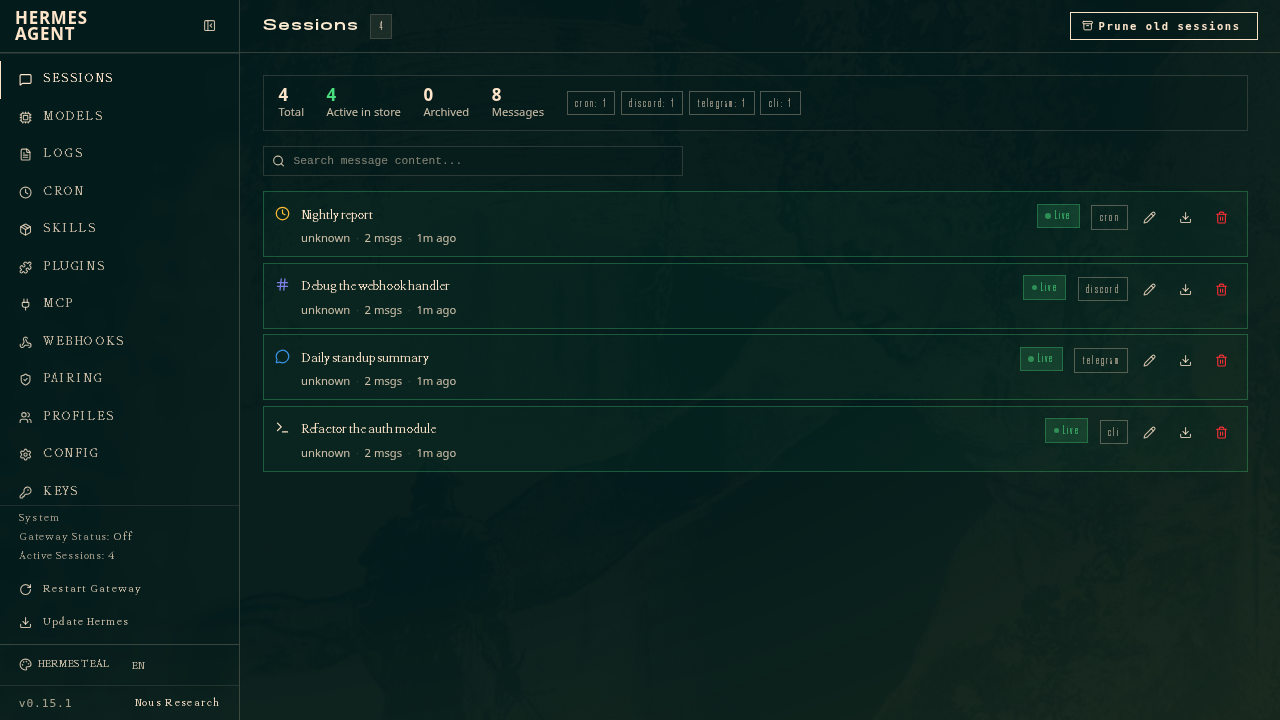
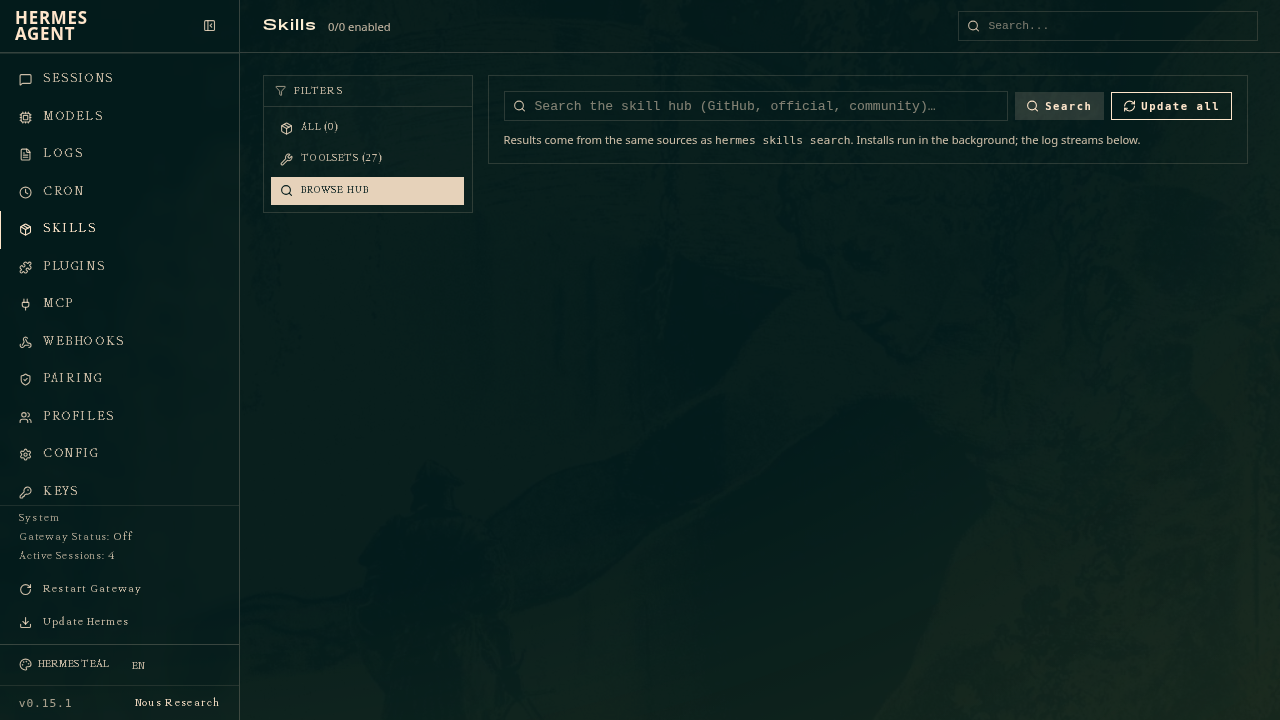
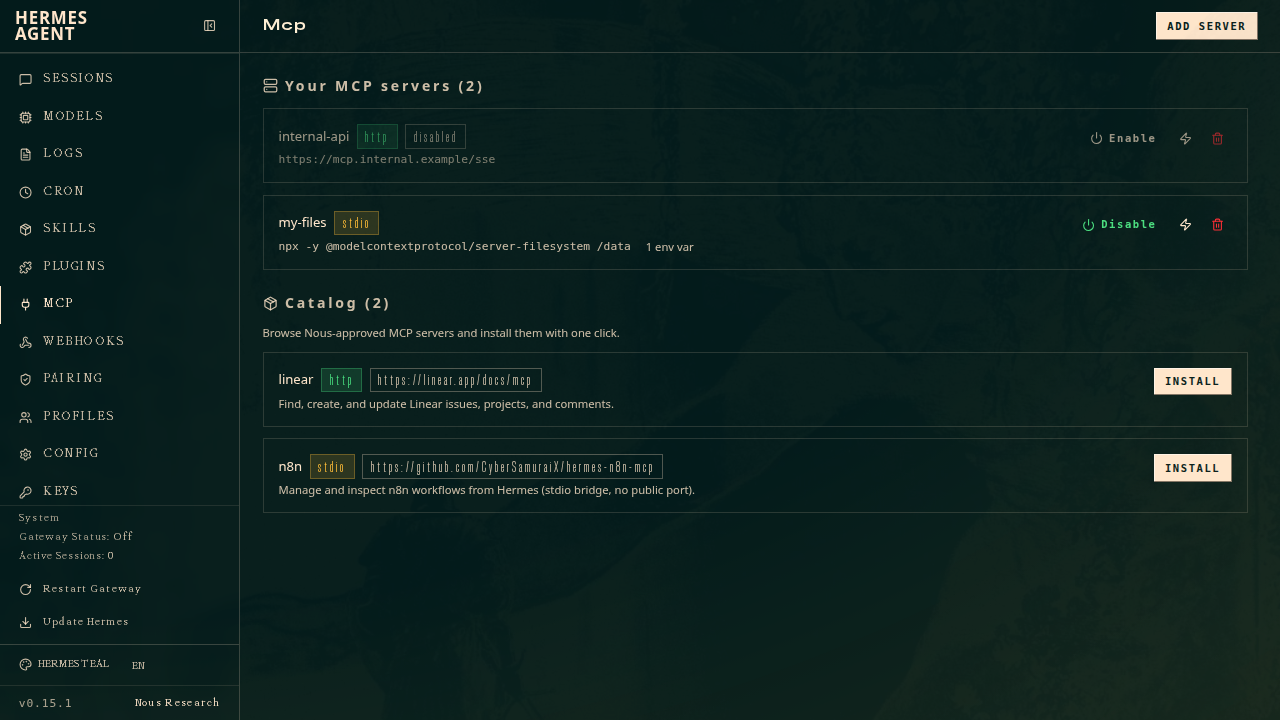
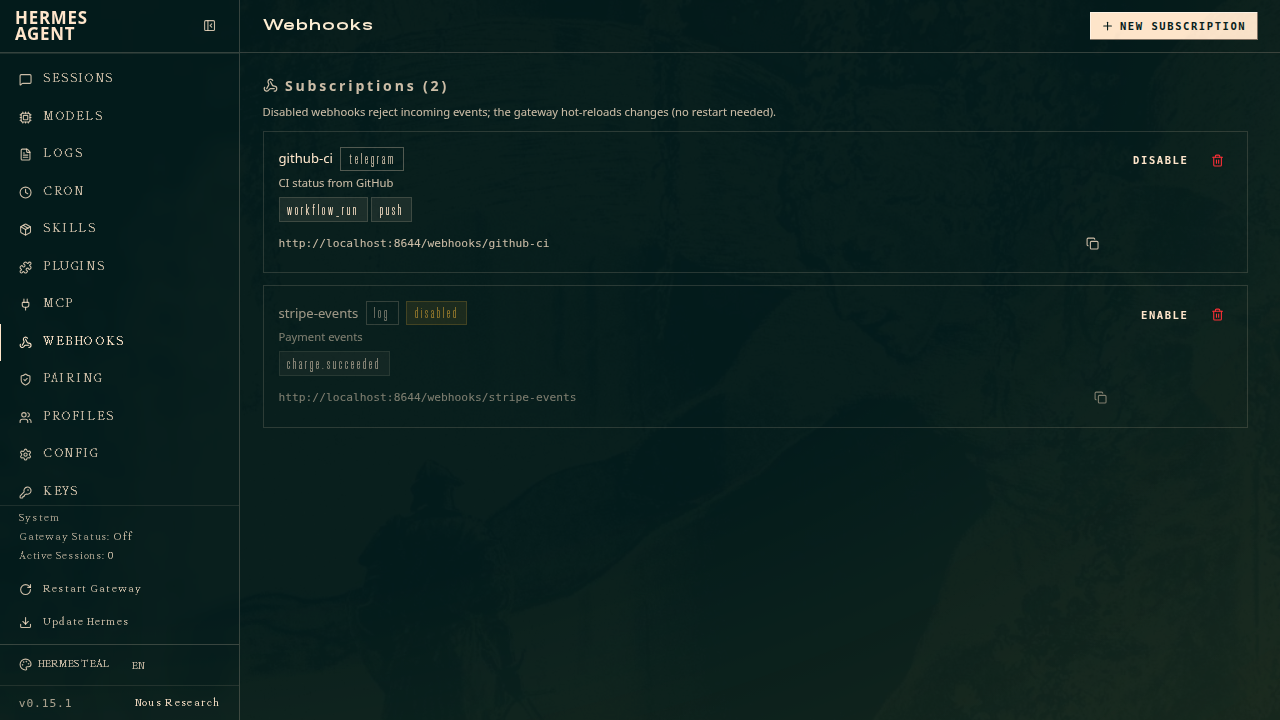
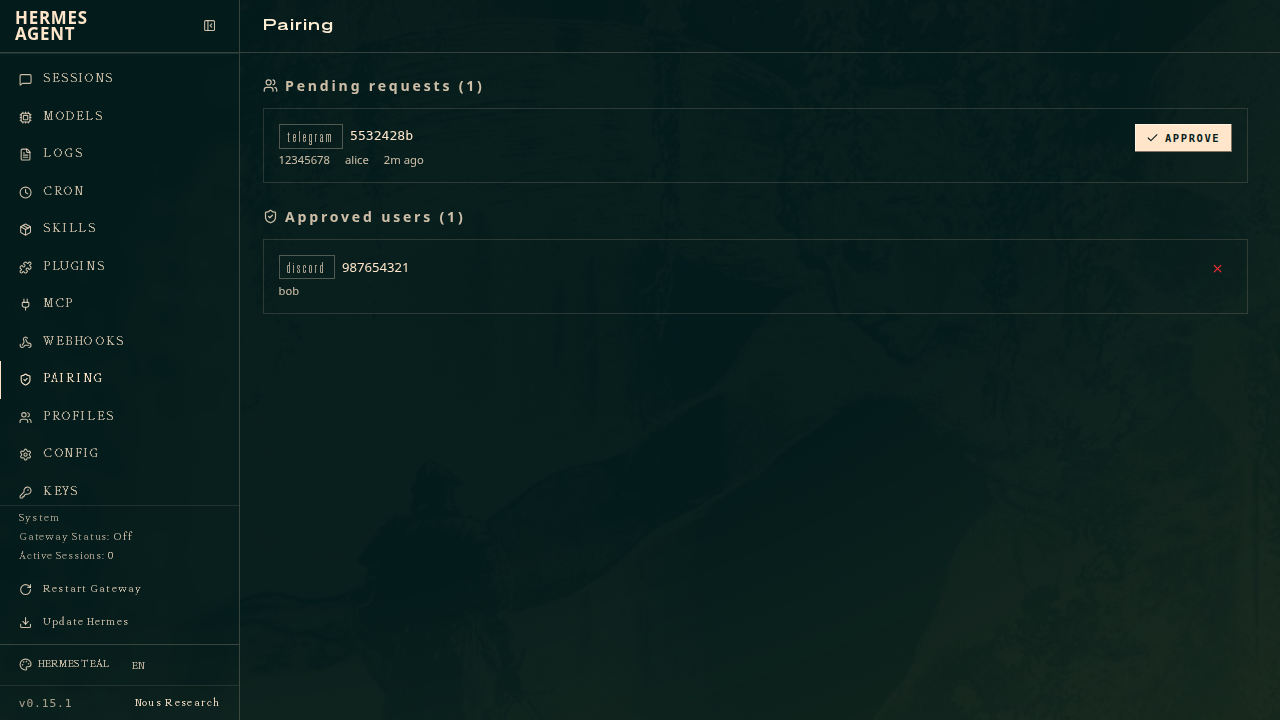
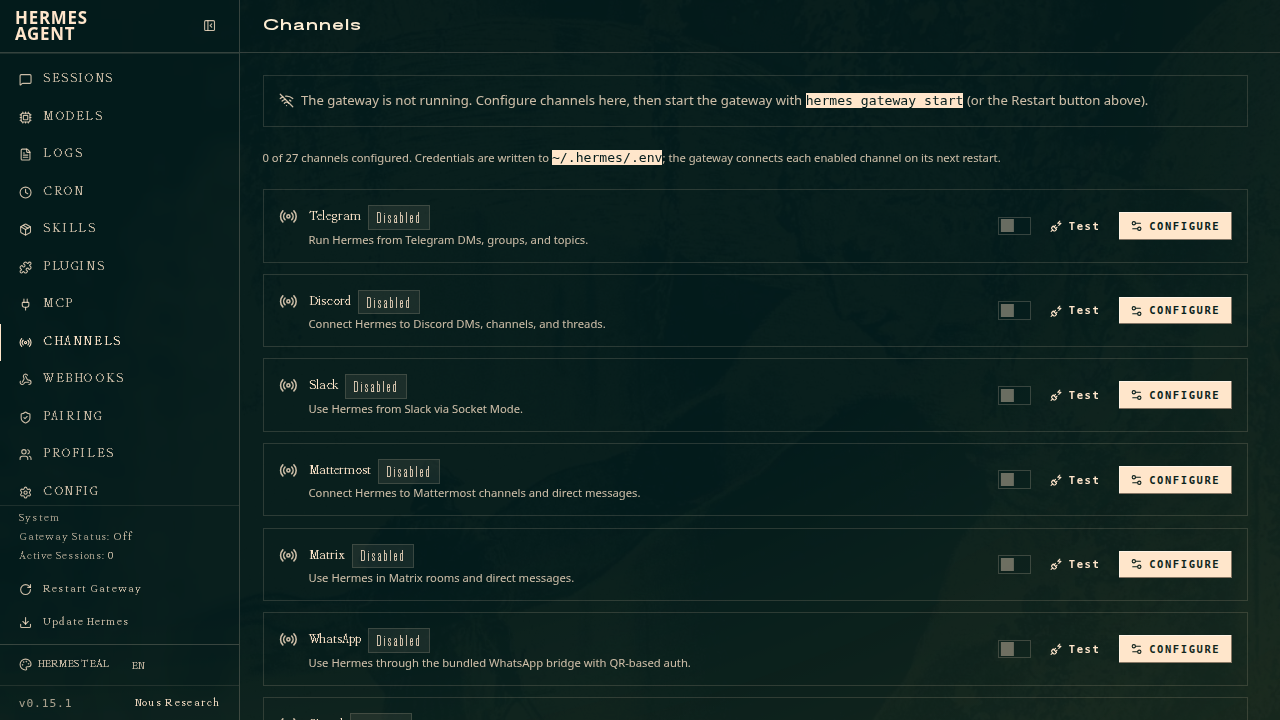
hermes dashboard --port 8080 --no-openA Note on “Isolated Mode”
If you start a dashboard with a named profile, like worker dashboard, it connects to the main console by default. But add the --isolated flag, and that profile gets its own dedicated console, completely separate from others. This is perfect when juggling multiple projects that shouldn’t mix.
One handy detail: a dashboard started from a profile alias keeps that profile as its fallback scope for the whole server lifetime. So a deep link that omits ?profile=—like a /chat?resume=<id> link—still opens under worker, and the embedded chat sees that profile’s MCP servers, model, and skills. An explicit ?profile= in the URL always wins.
One backend serves a whole host, so when hermes dashboard finds a live backend it cannot serve your typed --host/--port with, it refuses with exit 78 and names the owner. Stop that backend, or give the service its own dedicated server with --isolated. The Desktop app’s own loopback backends never claim host ownership, so the two can coexist without either flag. In a systemd unit, add Restart=always, RestartSec=10, and RestartPreventExitStatus=78 so the service parks on that deliberate refusal instead of looping with nothing listening.
Clock Skew and Token Leeway
Login tokens carry time claims (exp/nbf/iat), and a host whose clock lags the Portal’s can otherwise fail login. The dashboard tolerates a little clock skew by default: dashboard.oauth.token_leeway (config.yaml only) sets the tolerance in seconds applied to the Portal access token’s time claims during JWT verification. The default is 60 (RFC 7519 §4.1.4-4.1.6); 0 restores strict verification, and an invalid value (unparseable / negative / non-finite) fails closed to 0.
The self-hosted OIDC provider has the equivalent dashboard.oauth.self_hosted.id_token_leeway knob. It verifies the OpenID Connect ID token (RS256/ES256) against the discovered jwks_uri, with the iss and aud claims pinned to your configured issuer and client_id, and checks the time claims with the same 60-second leeway. Any value below 60 tightens it, 0 restores strict verification, and an invalid value fails closed to 0. Standard OIDC claims map onto the dashboard session.
Hub Actions Use the Target Profile’s Secrets
Here’s a security detail worth knowing. When you install or update a skill, install an MCP server, or set up a toolset from the dashboard’s hub, those actions run with the target profile’s own secret scope—its .env file and configured secret sources—not the dashboard process’s environment. That holds even when you’re acting on the default profile from the machine dashboard. In short: the right profile’s credentials get used, not whatever the dashboard happens to be running with.
Picking a Workspace for a Fresh Chat
A fresh chat starts wherever the dashboard process was launched—useless when you’re driving Hermes from a phone and want it in ~/code/foo. The rail’s workspace selector lists the same directories the Desktop sidebar knows: your explicit projects (hermes projects) and every discovered git repository (session-derived plus the desktop.repo_scan_roots scan), most recently active first, with an Other path… entry for anything else. The choice is remembered per profile and applies to the next New chat (a resumed session keeps its own working directory); the rescan button re-walks the discovery roots on the host, so a repo you just cloned over SSH shows up without a restart. A path that no longer exists is refused with an error instead of silently starting in the launch directory. Backed by GET /api/chat/workspaces and the cwd parameter of the /api/pty WebSocket.
Ignore the Old --insecure Flag
You might stumble across --insecure in older docs. It used to skip login, but it’s now dead. Even if you pass it, the system still demands authentication. Don’t try to sneak through the back door—just use a password or OAuth like a good citizen.
If Dependencies Break
FastAPI, Uvicorn, and the platform PTY helper are core Hermes dependencies. The web extra adds exact constraints for the HTTP stack. The pty extra is empty because its dependencies are already core. Standard PM setup includes web through all.
If these dependencies are damaged, run hermes pm repair and restart Hermes. For source setup, use the PM developer workflow. Messaging and voice extras are separate requests, not implied by all.
One more thing worth knowing: the web build is CPU- and memory-intensive (Vite 8’s Rust-native Rolldown bundler parallelizes across cores), so it is resource-bounded by default. The V8 heap is capped (--max-old-space-size, sized from the container’s memory limit) and the native bundler’s thread pool is limited to half the available cores (RAYON_NUM_THREADS), preventing the 200%+ CPU spikes and OOMs small VPS hosts otherwise hit during a build (#63338). Override with HERMES_WEB_BUILD_MAX_OLD_SPACE_SIZE / HERMES_WEB_BUILD_THREADS; set HERMES_WEB_BUILD_LIGHT=1 to tighten the caps (1 thread, 1 GB heap) when the host cannot spare full CPU.
Wrapping Up
The Web Dashboard swaps Hermes Agent’s steering wheel from keyboard to mouse, giving you a more intuitive way to manage your AI. Three big wins:
- Zero learning curve — no commands to memorize, the interface speaks for itself.
- Runs locally — your data stays put, safe and sound.
- Flexible configuration — ports, bind addresses, isolation—all adjustable to fit your workflow.
Practical tip: If you’re a first-timer, just run hermes dashboard with no extra flags. Get comfortable with the interface first. Once you know what you need, then start tweaking ports or binding addresses. And if you plan to access the dashboard remotely, set up password authentication first—don’t leave it naked on the public internet.
📖 Official Docs
This article is based on the official Hermes Agent documentation:Official docs › user-guide/features/web-dashboard